The practice of vulnerability assessment stands at the core of enterprise security. It enables lean teams to quantify risk and align resources with business priorities. In this paper we frame enterprise grade auditing as an operating discipline, not a one off exercise. Our aim is to deliver resilience, not just reports.
For years many firms treated vulnerability findings as compliance nudges. Now we demand measurable risk reduction. A mature program integrates people, process and technology. It balances speed and accuracy. It yields ROI through fewer incidents and faster containment.
The modern threat landscape rewards disciplined execution. Enterprise teams need scalable methods, clear playbooks and transparent risk scoring. This document presents an architecture for vulnerability assessment that stays robust as teams scale. It is designed for security leaders who demand results.
Related guidance: vulnerability scanning, remote code execution risks, and software bill of materials. For an authoritative external reference, see NIST patch management guidance. A repeatable vulnerability assessment programme is a core part of security operations engineering, security operations engineering, connecting discovery, prioritization, remediation, and continuous verification.
Vulnerability Assessment for Enterprise Security Teams
1.1 Scope and Boundaries
A lean security team must define what counts as a vulnerability. Scope includes on premise and cloud assets, data services and third party APIs. We also cover critical paths like authentication and authorization flows. The boundaries must be clear to avoid scope creep.
1.2 Audit Cadence
Cadence sets expectations for teams and business stakeholders. We propose a quarterly baseline with monthly micro-sprints on high risk domains. Threat-intelligence and asset-discovery feeds can support continuous prioritisation, while human review validates exposure, business context and remediation decisions. A disciplined cadence accelerates remediation and improves confidence.
Practical Vulnerability Assessment and Risk-Based Prioritisation
1. Establish an Accurate Asset and Exposure Baseline
Start with an authoritative inventory that joins cloud resources, servers, endpoints, network appliances, containers, applications, software components and third-party services to accountable owners. Record business service, environment, internet exposure, data sensitivity, identity dependencies, service criticality, operating-system and software versions, support status, and maintenance constraints. Reconcile scanner discovery with cloud control-plane inventories, endpoint management, CMDB records and software bills of materials. Unknown or unmanaged assets should be treated as an inventory and governance gap, not silently excluded from the assessment.
2. Run Authenticated Scans and Validate Findings
Use authenticated scanning where supported so the assessment can inspect installed packages, patch levels, configuration and local exposure more accurately than an unauthenticated network probe. Combine infrastructure scanning with application testing, container image scanning, dependency analysis and cloud configuration assessment. Record the scanner, plugin or feed version, scan time, credential coverage, excluded assets and any failed checks.
Validate high-priority findings before assigning remediation work. Confirm the affected product and version, whether the vulnerable component is enabled, whether the vulnerable code path is reachable, whether the asset is exposed, and whether a vendor mitigation or compensating control is in place. Check for duplicate findings across scanners and distinguish a confirmed vulnerability from a potential match based on a banner or version string.
3. Combine Severity, Exploitation Evidence and Local Context
CVSS communicates technical severity, but it is not a complete organisation-specific risk score. CISA’s Known Exploited Vulnerabilities (KEV) Catalog records vulnerabilities for which exploitation has been observed. FIRST’s Exploit Prediction Scoring System (EPSS) estimates the probability that exploitation activity for a published CVE will be observed in the wild over the next 30 days. EPSS is a population-level exploitation probability; it does not know whether the organisation runs the affected product, whether the vulnerable component is reachable, or what the impact would be locally.
Use these inputs as separate signals rather than multiplying EPSS by CVSS or treating either score as a final priority. A practical decision should combine:
- Known exploitation: whether the CVE is listed in KEV or there is credible evidence of exploitation relevant to the organisation.
- Exploit likelihood: EPSS probability and current threat intelligence, interpreted with its 30-day horizon and population-level limitations.
- Technical severity: CVSS base and relevant attack-vector, privilege and impact characteristics.
- Exposure and reachability: internet-facing status, network path, authentication requirements, vulnerable feature enabled, and access to the affected component.
- Business consequence: asset criticality, data sensitivity, safety or operational impact, and dependency on the affected service.
- Compensating controls: segmentation, WAF or virtual patching, access restrictions, monitoring and other controls that demonstrably reduce exposure.
- Remediation feasibility: patch availability, vendor support, testing requirements, maintenance windows and rollback options.
| Priority pattern | Example conditions | Expected treatment |
|---|---|---|
| Emergency response | Known exploitation or credible active exploitation; affected asset is exposed or highly critical; no effective mitigation | Immediate owner notification, exposure reduction, emergency change assessment and active compromise checks |
| Expedited remediation | High exploitation likelihood or severe weakness; vulnerable service is reachable; significant business impact | Prioritised patch or vendor mitigation, documented deadline and verification after change |
| Planned remediation | Vulnerability is confirmed but reachability or impact is limited by validated controls | Schedule within the risk-based remediation window and monitor for changes in exploitation or exposure |
| Exception or compensating control | No safe patch is currently available or remediation would create material service risk | Named risk acceptance, documented compensating controls, expiry date and recurring review |
Define remediation timeframes by priority and business service, then approve them through risk governance. Do not publish universal patch deadlines without considering regulatory scope, contractual commitments, vendor guidance and the organisation’s own risk appetite. A KEV listing or confirmed exploitation should trigger a prompt review even if the scanner’s severity score is lower than expected.
4. Remediate, Verify and Close the Loop
- Assign every validated finding to an asset or service owner, with a due date, affected version, recommended fix and evidence reference.
- Test patches and configuration changes in a representative environment, including application compatibility, dependencies, performance and rollback.
- Deploy through change control, prioritising exposed and business-critical assets. Where patching is not immediately possible, apply a documented mitigation such as disabling the vulnerable feature, restricting access or adding a validated virtual patch.
- Rescan or otherwise verify the actual installed state after remediation. A closed ticket or successful deployment job is not proof that the vulnerability is no longer present.
- Reopen findings when the fix failed, the vulnerable component remains enabled, or a new asset is discovered with the same exposure.
- Review exceptions on a fixed schedule and retire them when the patch, upgrade or compensating control becomes available.
5. Measure the Programme, Not Just the Scanner Output
Executive reporting should distinguish the number of findings from the risk actually reduced. Useful measures include asset inventory coverage, authenticated scan coverage, percentage of findings validated, exposure of KEV-listed vulnerabilities, age of critical internet-facing findings, remediation time by risk tier, recurrence after closure, exception age, and the proportion of fixes verified by rescanning. Report trends by business service and owner so leadership can see where risk is accumulating and where remediation is blocked.
Operational Playbooks for Secure Vulnerability Remediation
2.1 Playbook Architecture
We design remediation as a set of repeatable, modular playbooks. Each play includes triggers, owners, stepwise actions and exit criteria. We couple playbooks with dashboards that surface risk, progress and blockers. The architecture supports concurrent streams without chaos.
2.2 Runbooks and Automation
Automation handles low risk triage and evidence collection. Runbooks guide analysts through key actions. Automation pairs with human oversight to avoid blind fixes. This balance speeds remediation while preserving accountability.
The Resilience Maturity Scale
3.1 Definition
The Resilience Maturity Scale models how an organization responds to threats. It combines process discipline, technical controls and cultural readiness. The scale emphasizes practical improvements over theoretical capability. It maps security posture to business impact.
3.2 Stages and Metrics
We identify five stages: Initiation, Stabilization, Optimization, Integration, and Transformation. Each stage bears metrics for detection, containment and recovery. Progress depends on data quality, visibility and executive sponsorship. Leaders should target measurable shifts in risk rankings over time.
The Adversarial Friction Framework
4.1 Concept
Adversaries slow the defender by exploiting complexity. Our framework measures friction points in an environment. It considers attacker incentives and defender responses. The aim is to increase time to breach and reduce success probability.
4.2 Metrics and Implementation
We track friction across people, process and technology. Metrics include dwell time, lateral movement attempts and the effectiveness of containment. Implementation requires telemetry, artifact correlation and decision automation. The result is actionable risk signals rather than noise.
Zero Trust and Lateral Movement Controls
5.1 Network Layer Defenses
Zero Trust begins with continuous verification. We enforce identity, device posture and least privilege at every access point. Network layer controls must adapt to dynamic workloads and multi cloud environments. This reduces attack surface substantially.
5.2 Microsegmentation and API Hardening
Microsegmentation isolates workloads so an attacker cannot move easily. API hardening reduces exposure from container to service calls. Together they form a skeleton that supports rapid containment after compromises.
Threat Vectors and Cryptographic Agility
6.1 Threat Models
We anchor threat modeling in realistic attacker personas. We consider supply chain, insider risk and remote access vectors. The goal is to forecast likely attack paths and preempt them with controls.
6.2 Crypto Protocols and Key Management
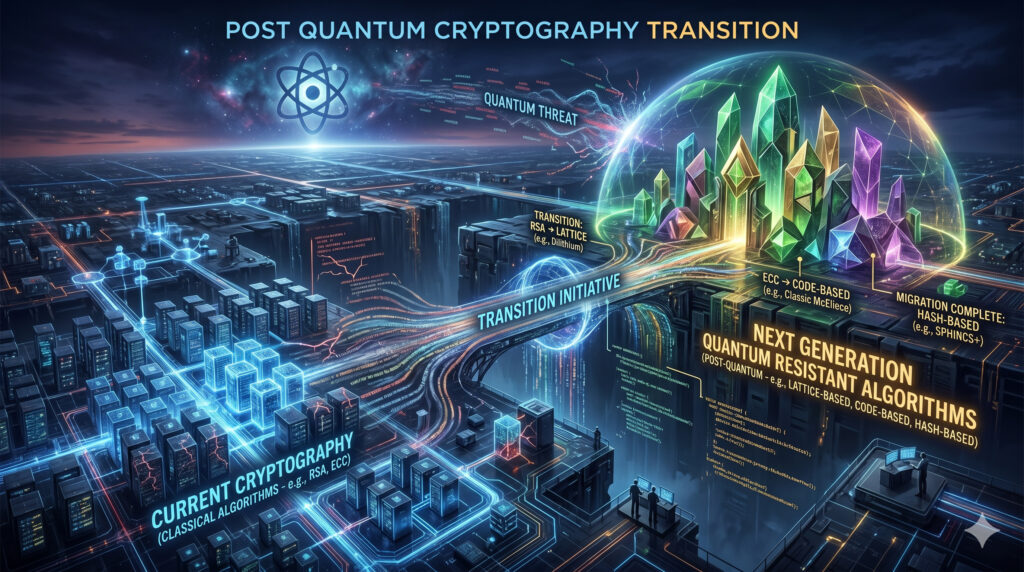
Cryptographic agility means updating algorithms without breaking services. We require automated key rotation, strong cryptographic primitives and verified opaque storage. This minimizes data exposure after a breach.
Architecture Landing: Infrastructure Nuances and ROI
7.1 ROI Frameworks
Security investments must show return. We compare direct savings from reduced incidents against intangible gains like faster time to market. We present a pragmatic model showing break even within 12 to 18 months.
7.2 Architecture Patterns
We map reference architectures to threat landscapes. Patterns cover on premises, cloud native and hybrid configurations. They emphasize automated evidence collection and auditable change control. The result is scalable resilience.
| Threat Level | Technical Protocols | Security ROI Metrics | Notes |
|---|---|---|---|
| Low | Routine patching, MFA | Modest cost reduction | Baseline hygiene |
| Medium | Network microsegmentation, API guards | Moderate ROI through fewer incidents | Requires automation |
| High | Zero Trust, rapid containment, cryptographic agility | High ROI via incident avoidance | Critical for data risk |
7.3 Audit Readiness Snapshot
We synthesize governance, people and technology into a single dashboard. The snapshot highlights gaps and ownership. It serves as a quarterly executive briefing.
Architect’s Defensive Audit
8.1 Audit Checklist
- Asset inventory across cloud and on prem is complete.
- Critical paths have verified access controls.
- Secrets are rotated and stored securely.
- Third party risk is assessed and monitored.
- Incident response playbooks are tested.
8.2 Executive KPIs
- Mean time to detect and mean time to contain improve over cycles.
- Patch cadence meets or beats risk-based targets.
- Breach surface exposure declines with each iteration.
- Audit findings go to remediation within agreed SLAs.
Chief Security Officer FAQ
9.1 How do we balance speed and risk in vulnerability remediation?
We prioritize patches by business impact and exposure. We automate triage for low risk items. High-risk items receive prompt escalation to the accountable service and risk owners, with executive involvement where business impact or accepted risk requires it. This balance reduces downtime and preserves user experience.
9.2 What metrics best demonstrate ROI from vulnerability programs?
We measure incident avoidance, remediation time, and changes in risk scores. We track resource leverage from automation and the cost of delayed fixes. A clear trend line shows ROI over time.
9.3 How do we handle third party risks in an enterprise setting?
We maintain supplier risk profiles and real time telemetry. We require evidence of patching and secure configurations. We monitor changes and enforce contractually required controls.
9.4 How can a lean team stay current with threat landscape changes?
We implement continuous learning and threat intel feeds. Teams can automate asset-to-CVE correlation and maintain a documented triage queue, while reviewing source quality and false matches. Regular tabletop exercises keep the team prepared.
9.5 What role does cryptographic agility play in resilience?
Cryptographic agility limits data exposure when algorithms become vulnerable. It enables rapid rekeying and algorithm migration. It protects both data in transit and at rest.
9.6 How do we prove executive sponsors value from vulnerability work?
We tie remediation outcomes to business outcomes like uptime and compliance readiness. We present clear dashboards and risk reduction narratives. The strategy aligns with strategic priorities.
9.7 How should we structure future investments in tooling?
Invest in telemetry, automation and orchestration. Prioritize platforms that integrate with existing security operations. Choose tools that reduce toil and improve accuracy.
9.8 What is the long term vision for vulnerability governance?
We aim for proactive risk containment, continuous improvement and adaptive defense. Governance evolves with the threat landscape and technology stack. It remains aligned to business risk.
Conclusion
Enterprise grade vulnerability assessment is a disciplined capability. It blends assessment, remediation and governance into one rhythm. Lean teams must embrace playbooks, maturity models and cryptographic agility to stay resilient. The core insight is simple: measure risk, automate where safe, and escalate when business value justifies it.
When executed with precision, vulnerability management yields predictable risk reduction. It also enhances stakeholder trust and accelerates delivery cycles. This is not a one time effort but a continuous program. The right architecture makes resilience scalable, repeatable and auditable.
The path to secure enterprise operations lies in disciplined auditing, actionable intelligence and relentless focus on reducing dwell time. By implementing the Resilience Maturity Scale and the Adversarial Friction Framework, leadership gains clarity and leverage. The payoff is a stronger security posture with demonstrable ROI.