Deep Visibility Architecture Implementing Extended EDR Capabilities Across Enterprise Linux Fleets
Extended EDR visibility across enterprise Linux fleets

Extended EDR visibility across enterprise Linux fleets
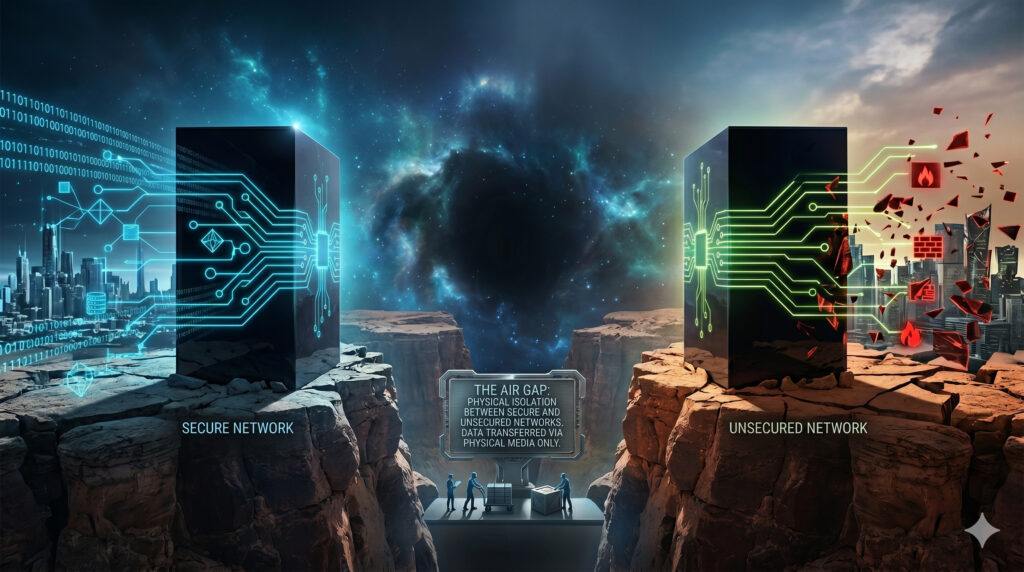
Decentralized SOC tying federated telemetry to risk
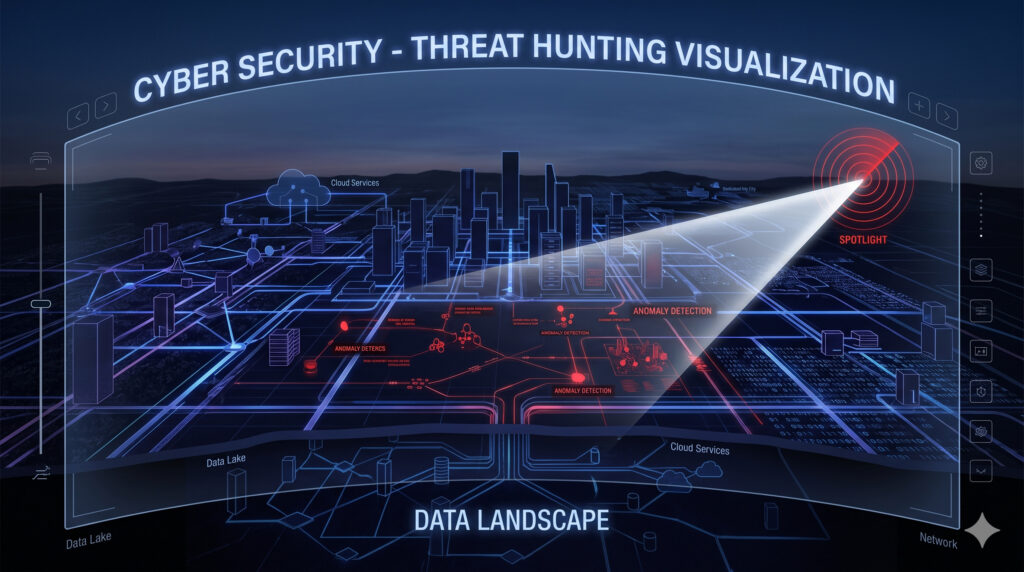
Correlating network and host logs for threat hunting
Continuous validation with automated breach simulations
Scaling continuous detection with automated threat emulation
Scaling open-source detection for enterprise SOCs
Automated triage for SOAR to tame endpoint alert floods
Safe automated endpoint isolation to prevent downtime
Mitigating SOC alert fatigue with ML triage
NetFlow telemetry for precision lateral threat hunting