Log Management Architecture Scaling Hot and Cold Data Repositories for Multi Year Retention
Scaling hot and cold log stores for multiyear retention
Architectural frameworks and engineering blueprints for the modern enterprise Security Operations Center. Articles deliver actionable strategies on optimizing SIEM and XDR data ingestion, refining detection engineering rules, leveraging SOAR automation, and mitigating alert fatigue across active defense teams.
Scaling hot and cold log stores for multiyear retention
Scaling automated triage to accelerate threat hunting
Automated network segmentation for active exploit triage
Reducing false positives with high-fidelity detections
EDR telemetry rules for memory inspection and triage
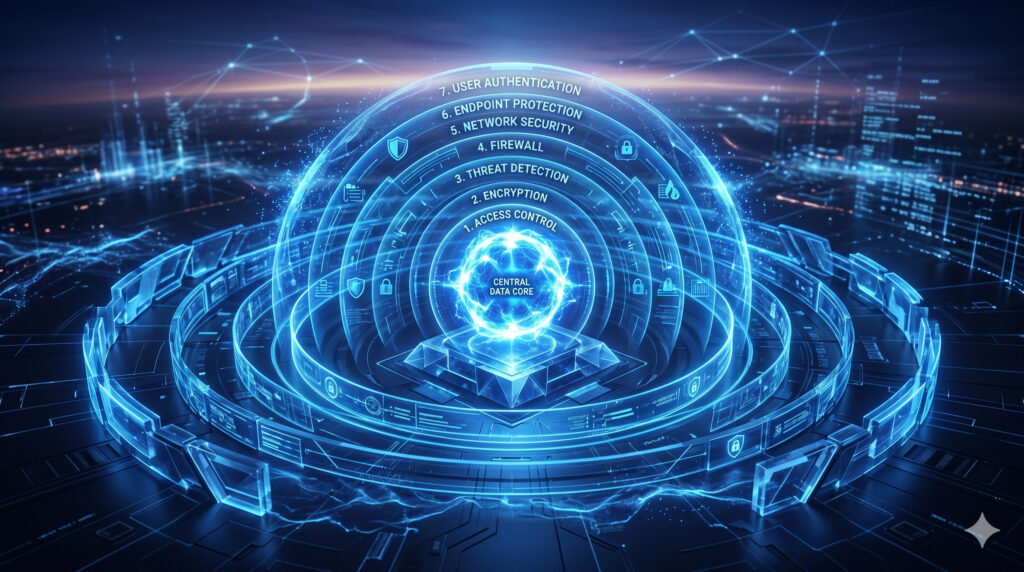
EDR penetration emulation: proving endpoint resiliency
Blueprints for resilient SIEM detection engineering
Tierless SOC design: optimizing incident response
Blueprints for enterprise honeypots: strategic deception
Extended EDR visibility across enterprise Linux fleets